
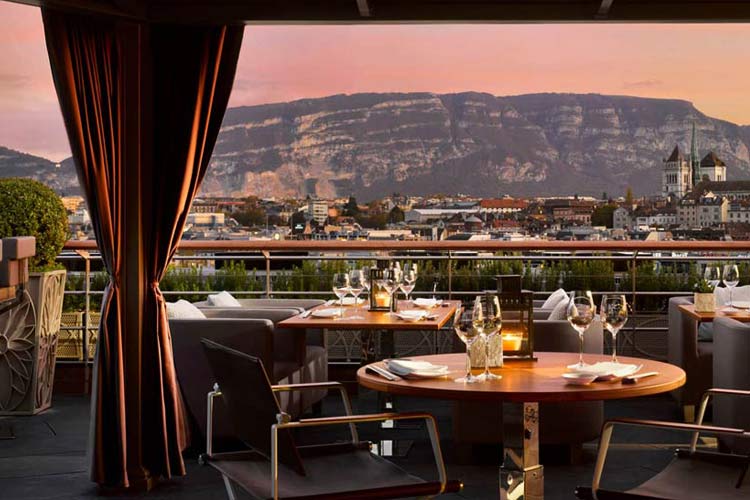
Often, the vibe at that rooftop bar or hotel terrace is as attractive as the view you’re looking at. The moment you sip your drink, you open up your MacBook or iPhone to upload photos, check reservations, respond to emails, and maybe plan the rest of your trip. We all know and love the convenience of public Wi-Fi, as a single click can connect your device to the network.
But that particular open Wi-Fi network might be the culprit for the issues occurring on your device. At such bars and hotels, these networks aren’t typically protected the way you expect them to be, as they prioritize convenience over security. Hence, throughout this article, we discuss what you as a Mac user should know about the potential risks and mitigation strategies regarding public networks.
The rooftop bar or the hotel lounge you’re sitting at is set for comfort above all. While you might expect the ultimate Wi-Fi protection, the reality of the situation is that there are hundreds of people who connect to it on a daily basis. As they’re often jam-packed, such locations provide an entry point for hackers.
Most networks stay open or use a single, simple password that you can find on menus or reception desks. That indicates minimal encryption. In such places where encryption is weak, your online activity is more exposed than ever. This can enable hackers to access your login pages, browsing history, and application traffic.
Crowds create the ultimate cover for those who want to steal data. The attacker can set up a hotspot mimicking the actual network, which most people wouldn’t even notice. If your MacBook is set to automatically connect again, it could easily connect to the wrong Wi-Fi without notifying you.
In crowded environments, such as on a rooftop, an attacker doesn’t even need to set up a fake network. Instead, they attach themselves in the middle of your connection, right between the Wi-Fi and your device. This is referred to as a man-in-the-middle attack, which allows someone to intercept the traffic flowing from or to your device.
As you have realized by now, public Wi-Fi risks are quite dangerous. They are the best hunting ground for malicious scripts, poisoned downloads, and silent installations. A fully compromised network can easily inject code into the web traffic and modify the files going back and forth. This makes the need to scan Mac for malware critical, which should become part of your routine check.
You should ideally run it before connecting to a public network and while you’re on it to scan for different malicious content, from spyware to hidden background processes. This comes in handy as sometimes your built-in protections are not enough to protect you from your desire to innocently browse, sync files, or log into your accounts.
Consistent checks will reduce the risk of delayed damage because even if malware appears to be inactive, it might be interfering with your system. So, a scan gives you a clearer picture of your device’s health after traveling or throughout your journey.
You might think that a rooftop hotel network comes with free Wi-Fi protection, but that’s just a myth. Remote workers and travelers usually check their messages, banking information, and work applications from the same device, making things that much riskier.
It is true that macOS comes with its own set of defenses, but that doesn’t mean it is invisible to attacks. Network-based threats usually bypass your device type entirely, so if an attacker can trick you into connecting to a fake hotspot, intercept traffic, or push a clone page onto your browser, they can potentially steal information without breaking through your macOS defenses.
Criminals have one objective, and that is to gain access across all platforms: identity theft, session takeover, and credentials stolen. That’s why they often try to push you to download “helpers” for Wi-Fi access, invoices, menus, or photos. They design things so they seamlessly fit into your workflow, whether that comes in the form of fake updates or Trojan applications.
Threat intelligence reporting also shows that acquiring malware remains a top priority for most attackers, another good reason not to trust public networks when you’re on macOS.
So, aside from knowing the risks of unsecured public Wi-Fi, you should aim to limit what other people on the same network can see, restrict shares, and check your device health. Our best practical habits and quick safety checklist include:
Rooftops and hotel terraces are a warm invitation for fun and relaxation, but they don’t come without potential danger. The danger seeps through the unseen, which is why public Wi-Fi is not always safe.
For a Mac user, awareness is the real deal. Knowing how to connect to a public Wi-Fi and how you might be exploited is already a step in the right direction. The objective is not to completely avoid such public networks, but to treat them as a temporary convenience instead of a trusted environment.
Browse all the cities & articles at The Rooftop Guide

Follow The Rooftop Guide